 By
SAP SuccessFactors has introduced an updated reference for designing permission roles in its 2H 2026 release, according to HR Tech Feed. The update, posted on October 18, 2026, is aimed at SuccessFactors administrators and implementation consultants who configure role-based access in Employee Central.
The reference provides a structured foundation for role design discussions and initial system configuration. It focuses on the most common permission roles used across the Employee Central Core business scenario, covering each role’s typical scope, purpose, and baseline permissions. SAP describes it as a starting point for building a secure, scalable, and well-governed permission model.
Why role design still trips up Employee Central projects
Permission roles in Employee Central control what HR staff, managers, and employees can see and do. A poorly designed role set creates immediate problems: payroll teams see data they should not, recruiters cannot open candidate files, or a single over-permissioned role becomes the default for everyone.
The challenge is that role design often happens late in an implementation, after business processes are already mapped. Teams then retrofit permissions onto existing workflows, which leads to exceptions, cloned roles, and audit findings. SAP’s updated reference appears intended to move that conversation earlier, giving consultants a baseline they can adapt rather than build from a blank sheet.
What the reference actually covers
The reference focuses on the Employee Central Core business scenario, which means it does not attempt to cover every SuccessFactors module. That scope matters. Payroll, recruiting, and onboarding have their own permission objects, and a reference built around Employee Central will not resolve access questions in those areas by itself.
For each common role, the reference describes the role’s typical scope, its purpose, and its baseline permissions. This is a design aid, not a technical implementation guide. Administrators still need to map those baseline permissions to their company’s specific organizational structure, data segmentation rules, and compliance requirements.
The practical value is in the starting point. Instead of asking “what should an HR generalist be able to do,” a consultant can open the reference, see the baseline for that role, and then adjust for local needs. That shortens design workshops and reduces the chance of missing a standard permission that later causes a support ticket.
Utilizing public domain imager, CC BY 3.0
What this means for HR and payroll teams
HR and payroll leaders should treat this update as a prompt to review their existing permission model, even if they are not planning a reimplementation. Role sprawl is common in mature SuccessFactors instances. Over time, administrators add permissions to solve immediate problems, and roles drift from their original purpose.
The reference gives teams a benchmark. If a current role grants far more access than the baseline for its equivalent in the reference, that is a signal to investigate. The same applies in reverse: if a role grants less, the team may have created workarounds outside the system, which carries its own risk.
Payroll teams have a particular interest here. Payroll data in Employee Central is sensitive, and permission errors can expose salary information to managers or peers. A reference that clarifies baseline permissions for roles touching payroll data helps payroll leads ask better questions during design and audit cycles.
Steps to take after the release
Administrators should first confirm that their instance has received the 2H 2026 release and that the updated reference is available in their documentation set. Release timing varies by data center, so availability may not be immediate for every customer.
Next, compare the reference roles against the roles currently active in the instance. Focus on the roles that map to Employee Central Core: HR administrator, HR generalist, manager, employee self-service, and any custom roles built from those templates. Document differences and flag any role where the current permissions exceed the baseline without a documented reason.
Finally, schedule a role design review with the implementation partner or internal security lead. The reference is a starting point, not a mandate. Companies with matrixed organizations, works councils, or strict data privacy rules will need to deviate from the baseline, and those deviations should be deliberate and recorded.
Common mistakes to avoid
One common mistake is treating the reference as a finished role set and assigning it without review. The baseline permissions are generic by design. They do not account for country-specific data protection rules, collective bargaining agreements, or company-specific approval chains.
Another mistake is ignoring the reference entirely because the instance is already live. Existing permission models accumulate technical debt. A new reference provides a low-cost opportunity to audit that debt and plan a cleanup, even if the cleanup happens over several releases.
A third mistake is expecting the reference to solve cross-module permission issues. Employee Central Core is one part of the SuccessFactors suite. Teams that also use Recruiting, Onboarding, or Payroll will still need to design those permission sets separately, using the Employee Central reference as a foundation rather than a complete answer.
Sources: HR Tech Feed
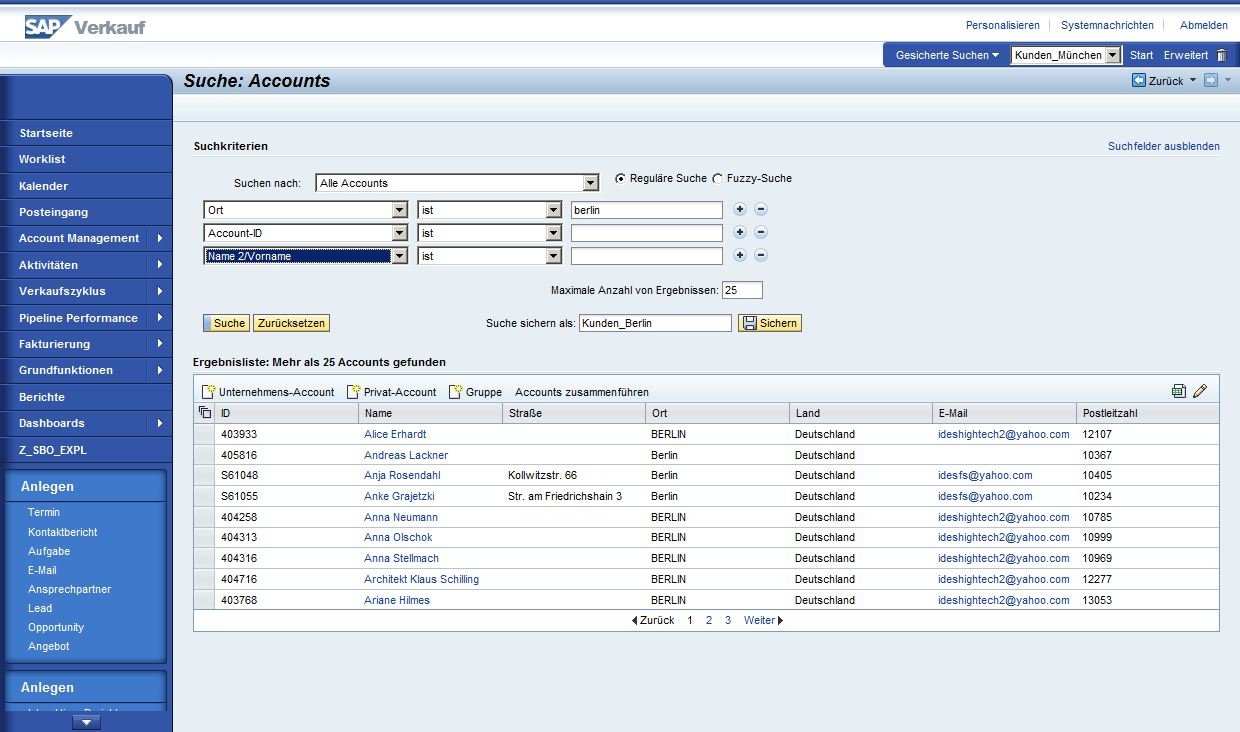
Photo: Suchseite by SALion, CC BY-SA 3.0